Architecture Overview

Built for infrastructure teams that need private cloud control without operational fragility.

VMease uses a modular control-plane design that separates user interaction, automation, infrastructure integration, operational state, and observability. This setup keeps operations reliable after deployment, makes governance easier to manage, and lets you scale easily from one site to many. It helps technical teams and decision makers trust that private cloud can work as one unified platform, not just a mix of scripts and consoles.

Layered control plane

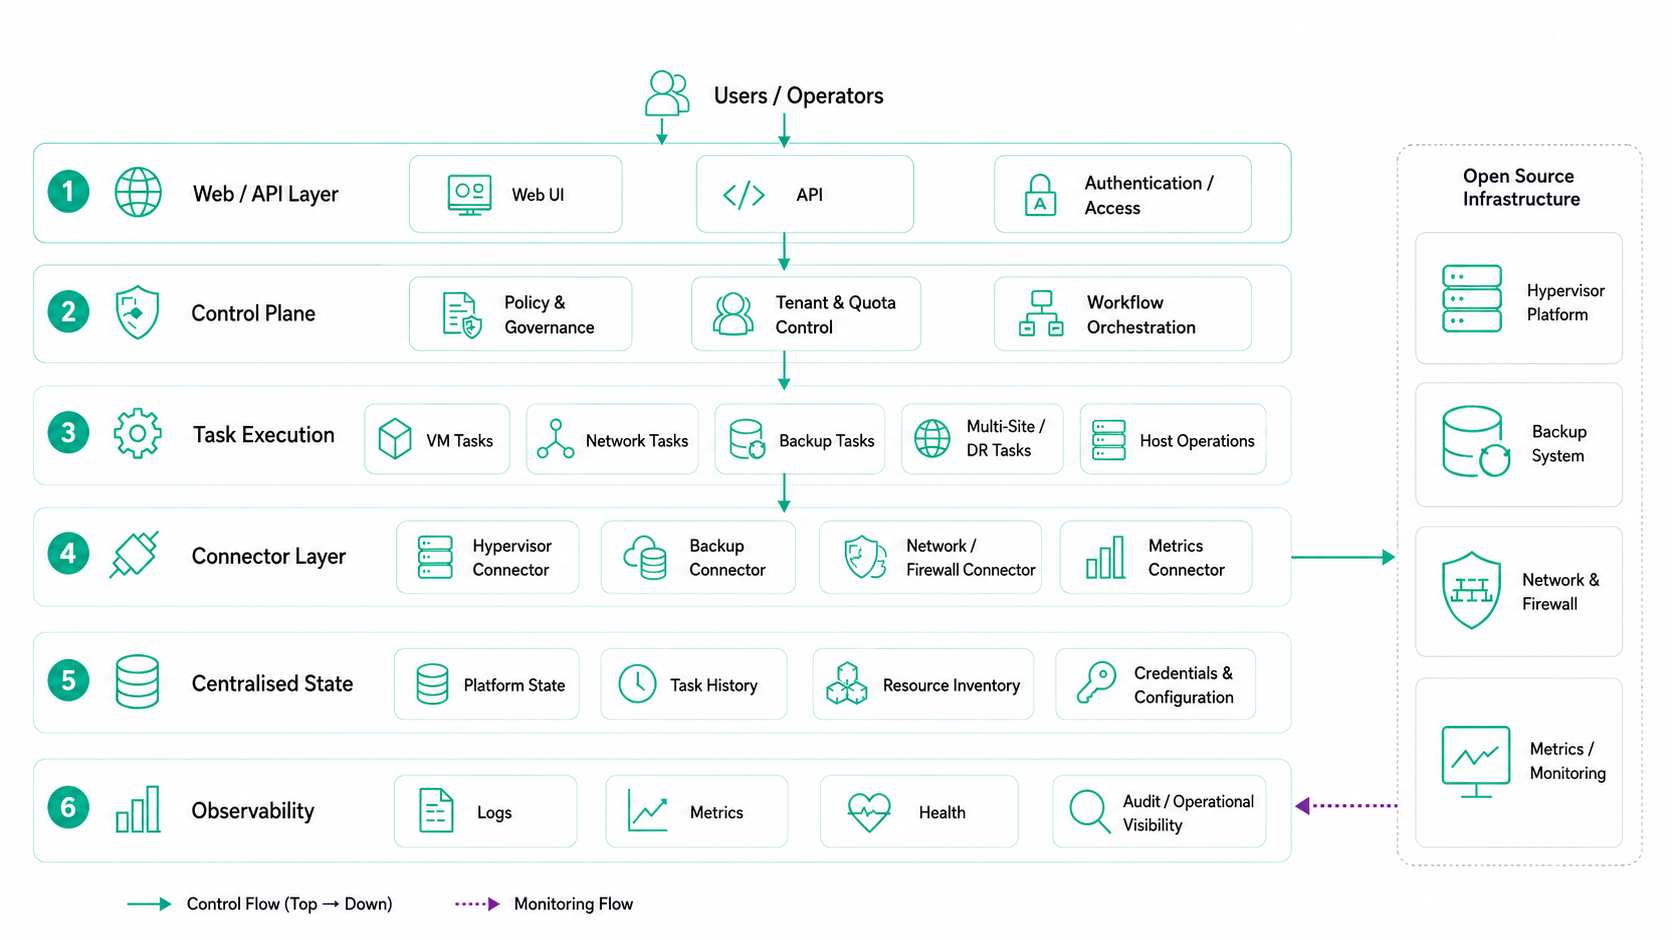
VMease layered control-plane architecture across access, governance, execution, and observability

The VMease control plane manages private cloud environments using a layered design. It separates user access, policy control, automation, infrastructure integration, platform state, and observability. Users and operators can use either the web interface or the API. The control plane handles governance, tenant boundaries, quota controls, and workflow orchestration, then sends tasks to specialized execution services. These services work with open-source tools like hypervisors, backup systems, network and firewall services, and metrics platforms. Centralized state, task history, resource inventory, credentials, and configuration help keep operations consistent. The observability layer collects logs, metrics, health, and audit data. By keeping these functions separate, VMease shows technical teams that it is more than just a portal. It is a governed automation platform built for repeatable operations, delegated administration, and reliable private-cloud service delivery.

VMease's architecture makes infrastructure management more controlled and repeatable. By separating control, execution, integration, and state, the platform helps reduce manual errors, improve visibility, and speed up troubleshooting. For organisations facing high VMware costs or public cloud sprawl, this design reduces risk, improves accountability, and provides a clearer path to private cloud delivery.

Architecture principles

Separation by design
The control plane, automation services, integration connectors, and state management are kept separate on purpose. This way, each part can change without compromising the stability of the whole platform.

Policy-led operations
Infrastructure actions follow governance rules such as roles, quotas, credential controls, and operational policies, rather than relying on ad hoc administrator access.

Tenant-aware governance
The platform maintains tenant and organisational boundaries, allowing teams to delegate administration while maintaining central oversight.

Centralised operational truth
Task states, activity history, and operational telemetry are brought together to create a consistent record for troubleshooting, audits, and service management.

Connector-led integration
Infrastructure interactions use reusable connectors. This helps avoid duplicate logic and makes operations more consistent across hypervisors, backup systems, networks, and security systems.

Resilience through modularity
Specialized automation services handle different parts of the infrastructure. This lowers the risk of large-scale failures and helps keep operations resilient across multiple sites.

Control plane at a glance

VMease uses a layered control plane that separates interface, orchestration, execution, infrastructure connectivity, and state. This helps teams see how changes are requested, checked, carried out, and tracked. It also avoids the confusion that comes from mixing portals and scripts. For technical evaluators, it shows the platform's design intent, not just a set of tools.

Modular automation services

Specialised automation services handle distinct parts of the infrastructure rather than relying on a single big system. This makes ownership clearer, establishes clearer boundaries for changes, and supports targeted troubleshooting. It also allows for upgrades and patches to be applied to each module without affecting other components. This approach keeps the platform maintainable, even under real production demands.

Automation and task execution model

VMease manages infrastructure operations at scale with asynchronous, task-driven execution. Requests are checked, sent to the right automation path, tracked until they finish, and recorded with clear status updates. The platform can run tasks in parallel and uses controls to prevent conflicting changes on the same resource. Long-running tasks are managed, so the platform stays responsive.

Resource-safe orchestration and background routines

The architecture includes safeguards to organize changes when resources might conflict, while still letting the system run efficiently. In addition to handling requests, it runs scheduled background tasks for health checks, housekeeping, and maintenance. This two-part approach improves reliability after deployment and reduces manual work. It also creates a stronger foundation for managed services and enterprise operations.

Connector-led infrastructure integration

VMease connects with Proxmox-based environments using a connector model that separates infrastructure details from higher-level workflows. This approach also works for integrating backup systems, network and firewall components, secure shell operations, and metrics pipelines. It makes behaviour and logging more consistent across all infrastructure actions and enables future expansion without redesigning the control plane.

Centralised state, observability and governance

Operational state is centralized so teams can see what was requested, what ran, and what happened across all services. Logging and telemetry provide clear visibility into failures and help track operations, rather than just showing isolated messages. Governance controls for access, credentials, and policy are managed in one place to reduce the risk of scattered admin practices. These foundations support audits, repeatable processes, and controlled delegated administration.

Unified design

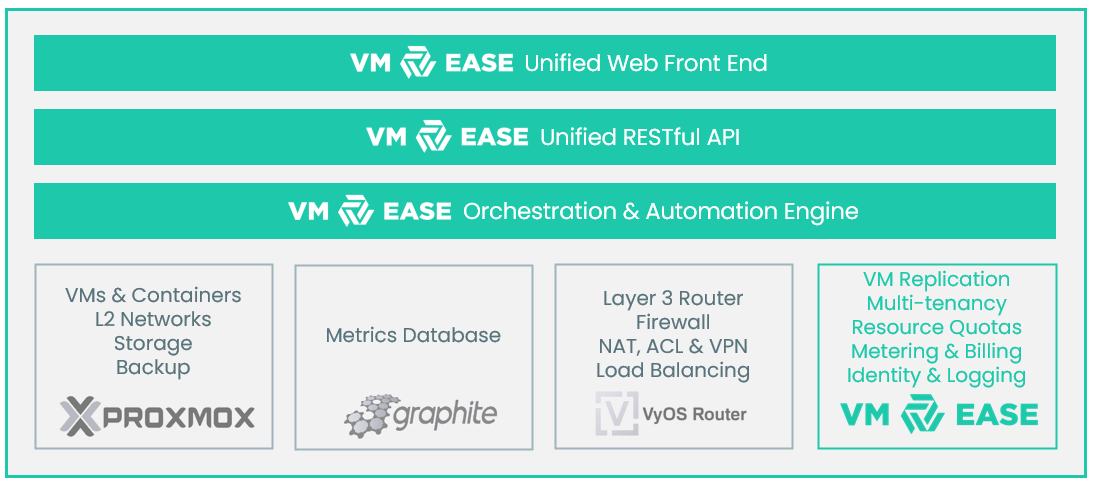
VMease unified private-cloud control layer integrating Proxmox, Graphite, VyOS, and platform services

The diagram overviews VMease as a single control layer for private cloud operations. The web front end gives users a unified experience, and the RESTful API lets developers access platform features programmatically. The orchestration and automation engine manages infrastructure workflows across the environment. Under this control layer, VMease connects to open-source tools such as Proxmox for virtual machines, containers, networking, storage, and backup; Graphite for metrics; and VyOS for routing, firewalling, NAT, ACLs, VPNs, and load balancing. VMease platform services add advanced features for large private clouds, including VM replication, multi-tenancy, resource quotas, metering and billing, identity management, and logging. These layers make VMease more than just a management interface. It is a governed automation platform that brings structure, visibility, and consistency to Proxmox-based private cloud environments.

FAQ

How are tenant boundaries maintained?

VMease is designed with tenant-aware governance in the control plane, so administrative actions are carried out within defined scope and policy. The RESTful API enforces this by validating all API calls for authorization, no matter where the request comes from. This supports delegated operations across teams or customers while keeping central control and reducing accidental cross-boundary changes.

How are failures surfaced and investigated?

Task outcomes, operational logs, and telemetry are combined to provide a transparent operational view. Teams can follow the history from request to outcome more quickly, which speeds up diagnosis and decreases reliance on individual operator knowledge.

Can this scale beyond a single lab cluster?

Yes. The architecture is designed for growth from single-cluster environments to larger multi-site estates by separating control-plane responsibilities, automation execution and infrastructure integration. That separation helps teams add scope without turning the platform into a single, fragile runtime. In practice, this supports staged expansion while retaining control and operational consistency.

What happens when tasks fail, or infrastructure APIs are unreliable?

The platform uses task-based execution with tracked status, so failed operations are visible rather than hidden in ad-hoc scripts. When dependencies are unstable, the architecture is designed to preserve operational state, clearly surface failure outcomes, and support controlled retry/recovery workflows. This reduces guesswork and helps operations teams resolve issues quickly.

How are infrastructure actions controlled once a user clicks something in the GUI?

User actions are not executed as direct, unmanaged API calls. Requests pass through a governed automation path, where they are validated, routed to the correct service domain, and tracked through to completion or failure. This provides a controlled execution chain with policy and operational context.

What prevents conflicting operations on the same resource?

The execution model supports parallelism across independent resources while applying resource-level safeguards to prevent conflicts. This means the platform can maintain high throughput without allowing unsafe overlap on the same infrastructure object. It is a key part of making automation predictable in production.

How are infrastructure credentials handled?

Credentials are managed through centralised governance with controlled access policies, rather than scattered across scripts or individual tools. Secrets are protected and used by authorised automation components as needed for infrastructure actions. This lowers exposure risk and improves operational control.

Can infrastructure actions be audited?

Yes. The architecture is designed around central task and operational visibility, giving a consistent record of requested actions and execution outcomes. That provides a practical audit trail for platform operations, change review and compliance-oriented governance.

Summary

VMease is designed as a modular private-cloud control plane, not just a single-purpose management console. Its design separates user interaction, task orchestration, infrastructure integration, and operational state, giving teams clearer control and less hidden complexity. This setup makes the platform easier to maintain as environments grow and reduces the fragility that often comes from using manual scripts and disconnected tools.

The platform's task-driven execution model gives a practical foundation for operational safety. Infrastructure changes are managed through governed automation pathways with visibility into progress, outcomes, and failure states. With background operational routines and centralised logging, this creates a more consistent operating model after deployment for platform teams, service providers, and internal IT operations.

For organisations that need to manage cost, resilience, and control, this architecture is both commercially relevant and technically strong. It supports tenant-aware governance, controlled credential use, and repeatable operations across Proxmox-based environments and related systems. This decreases operational risk, improves auditability, and lowers reliance on expensive or fragmented solutions. In short, VMease helps organisations run private cloud as a disciplined platform, not just a set of one-off admin tasks.

Ready to rethink private cloud?

Lower costs. Simplify operations. Deliver more.

Book a Strategy SessionTest Drive